5 min read
Prompt injection: defenses that work
Chunk-level allowlisting, output filtering, privilege separation for agents. Concrete defenses against retrieved-content injection, not the theory.
4 posts tagged security.
Chunk-level allowlisting, output filtering, privilege separation for agents. Concrete defenses against retrieved-content injection, not the theory.
Authentication is a fact you establish once. Authorization is a decision you make on every request — and that gap is where most access-control bugs live.
Vector search ranks by similarity, not permission. Why multi-tenant RAG leaks across tenants by default, and where the authorization check actually has to sit.
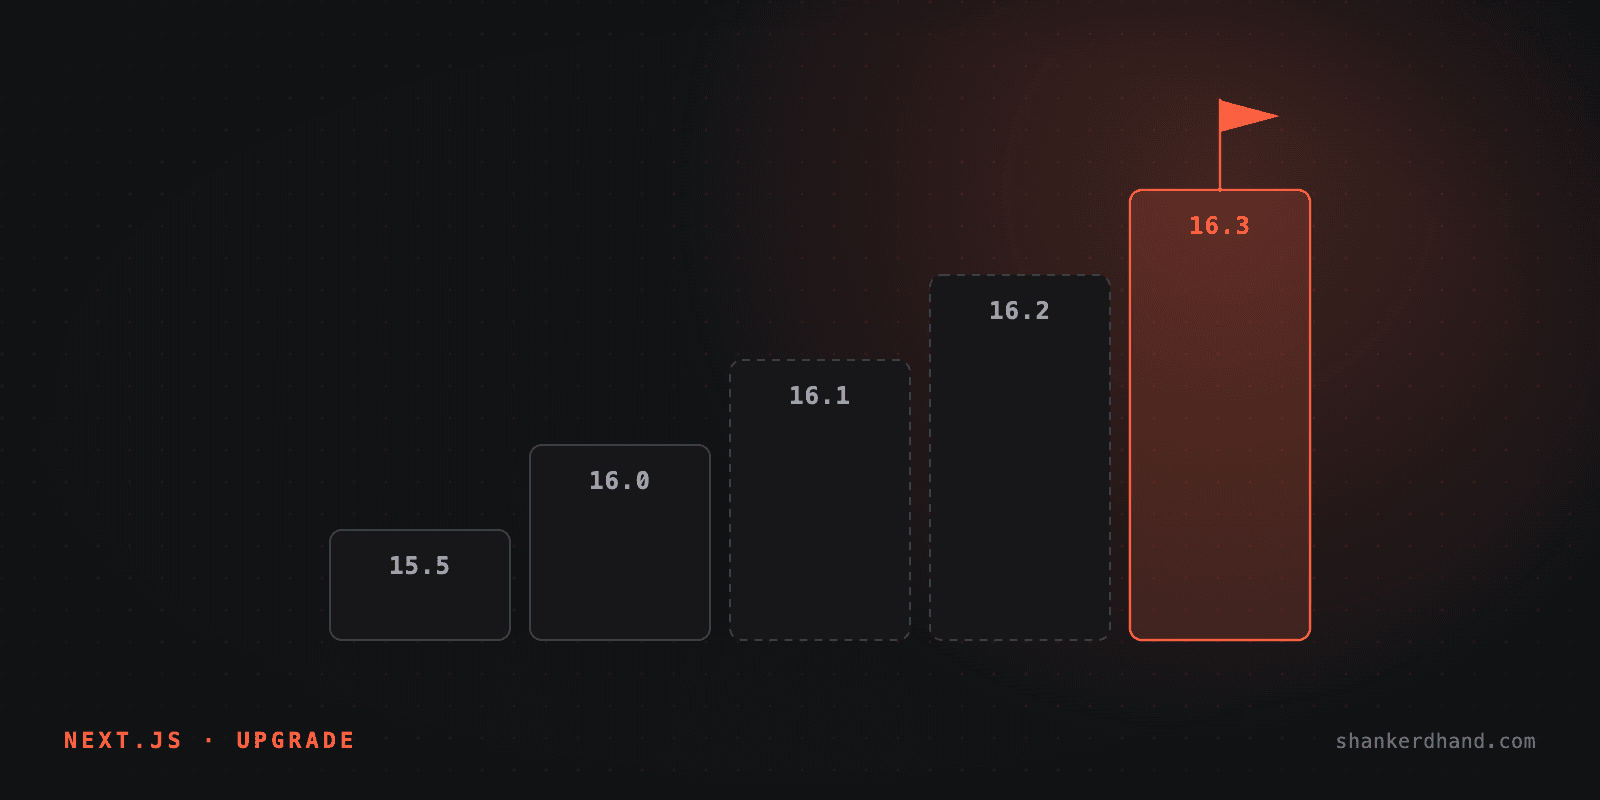
turbopackUseSystemTlsCerts was removed in Next.js 16.2: Turbopack now trusts OS certificates by default. Plus the two 16.3.3 security fixes: patch or migrate?